


[Nov 13, 2021] Download Free Juniper JN0-334 Real Exam Questions
Pass Your Exam With 100% Verified JN0-334 Exam Questions
Conclusion
There’s never a perfect time to make a career-changing decision. But this is certainly the best time to get ahead in your career using a reputable certification that will validate your competency in managing Juniper Networking solutions and products. It is a big decision that starts with choosing the right designation, preparing for the required exam, and passing it. And that exam today is the Juniper JN0-334, which covers all the aspects you need to build a fruitful career. This post has attempted to cover everything you need to know to clear JN0-334 exam. So, the remaining percentage is solely a personal decision. Make it happen today!
NEW QUESTION 46
Which two session parameters would be used to manage space on the session table? (Choose two.)
- A. TCP MSS
- B. TCP RST
- C. high watermark
- D. low watermark
Answer: C,D
NEW QUESTION 47
Click the Exhibit button.
Which two statements describe the output shown in the exhibit? (Choose two.)
- A. Node 1 is passing traffic for redundancy group1.
- B. Node 0 is passing traffic for redundancy group 1.
- C. Redundancy group 1 was administratively failed over.
- D. Redundancy group 1 experienced an operational failure.
Answer: A,C
NEW QUESTION 48
Exhibit.
Referring to the exhibit, which statement is true''
- A. Malicious HTTP file downloads are always blocked
- B. Malicious HTTP file downloads are never blocked
- C. Hosts are always able to communicate through the SRX Series device no matter the threat score assigned to them on the infected host feed.
- D. Hosts are unable to communicate through the SRX Series device after being placed on the infected host feed with a high enough threat score
Answer: C
NEW QUESTION 49
Which two protocols are supported for Sky ATP advanced anti-malware scanning? (Choose two.)
- A. MAPI
- B. POP3
- C. SMTP
- D. IMAP
Answer: C,D
Explanation:
Explanation
NEW QUESTION 50
Your network uses a remote e-mail server that is used to send and receive e-mails for your users In this scenario. what should you do to protect users from receiving malicious files through e-mail?
- A. Deploy Sky ATP IMAP e-mail protection
- B. Deploy Sky ATP POP3 e-mail protection.
- C. Deploy Sky ATP SMTP e-mail protection
- D. Deploy Sky ATP MAPI e-mail protection
Answer: A
NEW QUESTION 51
Click the Exhibit button.
You have an IPsec tunnel between two devices. You clear the IKE security associations, but traffic continues to flow across the tunnel.
Referring to the exhibit, which statement is correct in this scenario?
- A. The traffic is no longer encrypted
- B. The IPsec security association is independent from the IKE security association
- C. The IKE security association immediately reestablishes
- D. The traffic is using an alternate path
Answer: A,B
NEW QUESTION 52
Exhibit.
The output shown in the exhibit is displayed in which format?
- A. sd-syslog
- B. OWELF
- C. syslog
- D. binary
Answer: A
NEW QUESTION 53
When working with network events on a Juniper Secure Analytics device, flow records come from which source?
- A. mirror
- B. SPAN
- C. tap port
- D. switch
Answer: B
NEW QUESTION 54
Referring to the configuration shown in the exhibit, which two statements are true? (Choose two)
- A. The syslog is configured for a user facility
- B. The log is being stored on the local Routing Engine
- C. The syslog is configured for an info facility
- D. The log is being sent to a remote server
Answer: A,C
NEW QUESTION 55
A routing change occurs on an SRX Series device that involves choosing a new egress interface In this scenario, which statement is true for all affected current sessions?
- A. The current sessions do not change
- B. The current sessions are torn down only if the policy-rematch option has been enabled.
- C. The current sessions are torn down and go through first path processing based on the new route.
- D. The current sessions might change based on the corresponding security policy
Answer: C
NEW QUESTION 56
Which two functions are performed by Juniper Identity Management Service (JIMS)? (Choose two.)
- A. JIMS synchronizes Active Directory authentication information between a primary and secondary JIMS server.
- B. JIMS forwards Active Directory authentication information to SRX Series client devices.
- C. JIMS collects and maintains a database of authentication information from Active Directory domains.
- D. JIMS replicates Active Directory authentication information to non-trusted Active Directory domain controllers.
https://www.juniper.net/documentation/en_US/junos/topics/reference/configuration-statement/services-user-identification-identity-management-connection-primary.html
Answer: A,C
NEW QUESTION 57
Your network uses a remote e-mail server that is used to send and receive e-mails for your users.
In this scenario, what should you do to protect users from receiving malicious files thorugh e-mail?
- A. Deploy Sky ATP POP3 e-mail protection
- B. Deploy Sky ATP SMTP e-mail protection
- C. Deploy Sky ATP IMAP e-mail protection
- D. Deploy Sky ATP MAPI e-mail protection
Answer: B
NEW QUESTION 58
Click the Exhibit button.
You have implemented SSL proxy client protection. After implementing this feature, your users are complaining about the warning message shown in the exhibit.
Which action must you perform to eliminate the warning message?
- A. Import the SRX self-signed CA certificate into the client Web browsers.
- B. Import the SRX self-signed CA certificate into the SRX certificate public store.
- C. Configure the SRX Series device as a trusted site in the client Web browsers.
- D. Regenerate the SRX self-signed CA certificate and include the correct organization name.
Answer: A
NEW QUESTION 59
Click the Exhibit button.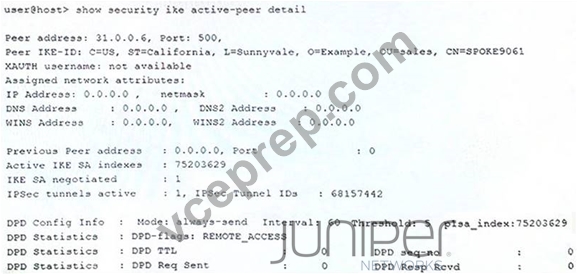
A customer would like to monitor their VPN using dead peer detection.
Referring to the exhibit, for how many minutes was the peer down before the customer was notified?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: C
NEW QUESTION 60
You are troubleshooting advanced policy-based routing (APBR).
Which two actions should you perform in this scenario? (Choose two.)
- A. Verify that the APBR profiles are applied to the egress zone.
- B. Inspect the application system cache for the application entry.
- C. Verity inet.0 for correct route leaking.
- D. Review the APBR statistics for matching rules and route modifications.
Answer: B,D
NEW QUESTION 61
Which two settings must be enabled on the hypervisor in a vSRX deployment to ensure proper chassis cluster operation? (Choose two)
- A. Control links must have an MTU of 9000.
- B. Fabric links must have an MTU of 9000
- C. Fabric links must operate in promiscuous mode.
- D. Control links must operate in promiscuous mode.
Answer: B,D
NEW QUESTION 62
What are two types of attack objects used by IPS on SRX Series devices? (Choose two.)
- A. protocol anomaly-based attacks
- B. DDoS-based attacks
- C. signature-based attacks
- D. spam-based attacks
Answer: A,C
NEW QUESTION 63
Click the Exhibit button.
You have configured your SRX Series device to receive authentication information from a JIMS server. However, the SRX is not receiving any authentication information.
Referring to the exhibit, how would you solve the problem?
- A. Use the JIMS Administrator user interface to add the SRX device as client.
- B. Update the IP address of the JIMS server
- C. Generate an access token on the SRX device that matches the access token on the JIMS server.
- D. Change the SRX configuration to connect to the JIMS server using HTTP.
The device obtains an access token after it authenticates to the JIMS server. The device must use this token to query JIMS for user information.). Token is used for the user identity information after if authentication is successful and in this case it is stuck in the authentication. Following is the link. (https://www.juniper.net/documentation/en_US/junos/topics/topic-map/security-user-auth-configure-jims.html
Answer: A
NEW QUESTION 64
Click the Exhibit button.
Referring to the exhibit, what will happen if client 172.16.128.50 tries to connect to destination
192.168.150.111 using HTTP?
- A. The client will be denied by policy p1.
- B. The client will be permitted by policy p2.
- C. The client will be denied by policy p2.
- D. The client will be permitted by policy p1.
Answer: D
NEW QUESTION 65
You have deployed JSA and you need to view events and network activity that match rule criteria. You must view this data using a single interface. Which JSA feature should you use in this scenario?
- A. Network Activity
- B. Assets
- C. Log Collector
- D. Offense Manager
Answer: A
NEW QUESTION 66
Click the Exhibit button.
You have implemented SSL proxy client protection. After implementing this feature, your users are complaining about the warning message shown in the exhibit.
Which action must you perform to eliminate the warning message?
- A. Import the SRX self-signed CA certificate into the client Web browsers.
- B. Import the SRX self-signed CA certificate into the SRX certificate public store.
- C. Configure the SRX Series device as a trusted site in the client Web browsers.
- D. Regenerate the SRX self-signed CA certificate and include the correct organization name.
Answer: A
NEW QUESTION 67
What are two management methods for cSRX? (Choose two.)
- A. CLI
- B. J-Web
- C. Contrail
- D. Network Director
Answer: A,B
NEW QUESTION 68
Click the Exhibit button.
Referring to the configuration shown in the exhibit, which two statements are true? (Choose two.)
- A. The log is being sent to a remote server.
- B. The syslog is configured for an info facility.
- C. The log is being stored on the local Routing Engine.
- D. The syslog is configured for a user facility.
Answer: A,D
Explanation:
https://www.juniper.net/documentation/en_US/junos/topics/reference/configuration-statement/syslog-edit-system.html
NEW QUESTION 69
You are asked to convert two standalone SRX Series devices to a chassis cluster deployment. You must ensure that your IPsec tunnels will be compatibla with the new deployment.
In this scenario, which two interfaces should be used when binding your tunnel endpoints? (Choose two.)
- A. lo0
- B. pp0
- C. ge
- D. reth
Answer: C,D
NEW QUESTION 70
......
Juniper JN0-334 Exam Certification Details:
| Exam Name | Security Specialist |
| Exam Registration | PEARSON VUE |
| Number of Questions | 65 |
| Exam Price | $300 USD |
| Passing Score | Variable (60-70% Approx.) |
| Exam Code | JN0-334 JNCIS-SEC |
| Recommended Training | Juniper Security |
| Sample Questions | Juniper JN0-334 Sample Questions |
| Duration | 90 minutes |
Juniper JN0-334 Exam Topics:
| Section | Objectives |
|---|---|
| Juniper Identify Management Service (JIMS) | Identify concepts, general features, or functionality of JIMS
Demonstrate knowledge of how to configure, monitor, or troubleshoot JIMS |
| Advance Threat Prevention (ATP) | Identify the concepts, benefits, or operation of Sky ATP
Demonstrate knowledge of how to configure, monitor, or troubleshoot Sky ATP Identify the concepts, benefits, or operation of JATP
Demonstrate knowledge of how to configure, monitor, or troubleshoot JATP |
| High Availability (HA) Clustering | Identify the concepts, benefits, or operation of HA
Demonstrate knowledge of how to configure, monitor, or troubleshoot clustering |
| Security Policies (Advanced) | Identify the concepts, benefits, or operation of security policies
Demonstrate knowledge of how to configure, monitor, or troubleshoot security policies |
| Application Security | Identify application security concepts
Demonstrate knowledge how to configure, monitor, or troubleshoot application security Identify application IDP/IDS concepts
Demonstrate knowledge how to configure, monitor, or troubleshoot IDP/IDS |
| SSL Proxy | Identify concepts, general features, or functionality of SSL Proxy
Demonstrate knowledge of how to configure, monitor, or troubleshoot SSL proxy |
| Virtual SRX or cSRX | Describe concepts, general features, or functionality of virtualized security using vSRX or cSRX
|
| Juniper Secure Analytics (JSA) | Identify concepts, general features, or functionality of JSA
|
JN0-334 Dumps 100 Pass Guarantee With Latest Demo: https://www.vceprep.com/JN0-334-latest-vce-prep.html